Why AI Needs a New Layer of Security — and Why We’re Building It in Stealth
Why AI Needs a New Layer of Security — and Why We’re Building It in Stealth
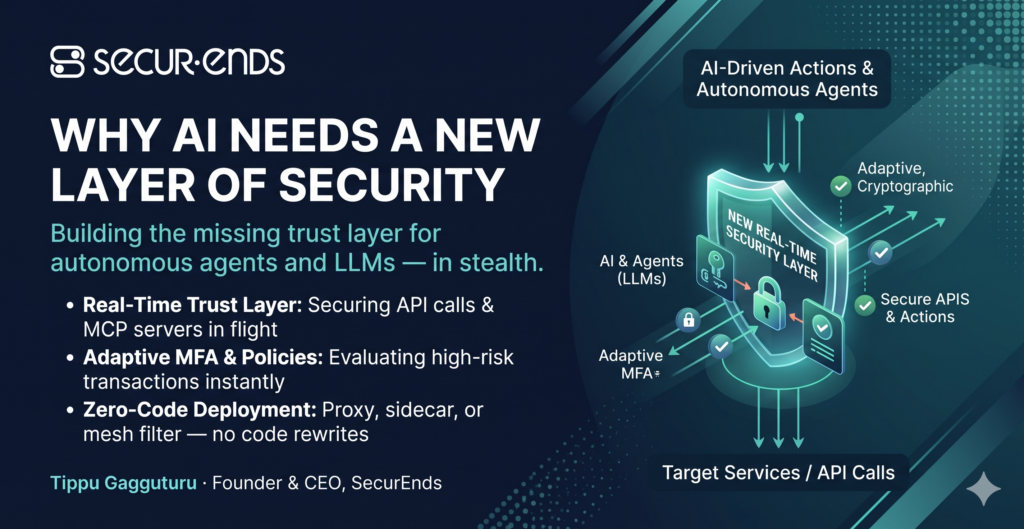
The rise of MCP servers, LLMs, and autonomous agents has unlocked incredible potential. AI is no longer just answering questions — it’s taking actions, calling APIs, and moving data. But with that power comes a new reality:
- Every AI agent is effectively an API client.
- Every API call could be a high-risk transaction.
Yet, today’s security models aren’t built for this world.
The Gaps in Today’s AI Security
- Static API Keys & Tokens: Single-factor credentials that can be stolen and replayed.
- OAuth Grants: Long-lived and coarse-grained; not built for fine-grained, real-time enforcement.
- Traditional API Security Tools: Focused on monitoring after the fact, not preventing risk at the moment of action.
In short, there’s no real-time trust layer for AI-driven interactions.
What We’re Building
While still in stealth mode, here’s a glimpse of the vision:
- Adaptive MFA Enforcement: Every API call is evaluated in real time. Safe calls pass seamlessly, high-risk calls are challenged.
- Payload-Aware Policies: Transactions can be blocked or allowed based on payload attributes (e.g., data type, record count, or sensitivity). Bulk exports, privileged role creations, or large fund transfers can be allowed or denied according to business and compliance rules.
- Proof-of-Possession Security: Credentials alone aren’t enough. Requests are cryptographically bound to the client, preventing token replay or theft.
- Zero-Code Deployment: Runs as a proxy, sidecar, or mesh filter — no code rewrites for clients or servers.
- Audit-Ready Insights: Every decision logged with risk score, payload context, policy outcome, and traceability for compliance.
Real-World Use Cases
- Financial Services: Step-up MFA for high-value transfers, new payee creation, or unusual agent behavior.
- Healthcare: Block or challenge bulk patient data exports triggered by LLM-driven automations.
- Enterprise SaaS: Control Salesforce or Workday API usage by MCP servers to prevent mass exfiltration.
- Cloud Security: Require adaptive MFA and payload checks for IAM role creation, key rotation, or storage deletions in AWS, Azure, or GCP.
Why Stealth?
This isn’t about chasing hype. It’s about building the missing trust layer for AI — carefully, with the right partners, and with the precision this space demands.
We’re in stealth because timing matters. When this technology surfaces, it won’t be another buzzword — it will be a new foundation for securing AI-driven enterprises.
Stay tuned. The next era of AI Security is closer than you think.
Visit SecurEnds.