Automated Access Deprovisioning: How to Verify Access Removal
Automated Access Deprovisioning: How to Verify Access Removal
TL;DR
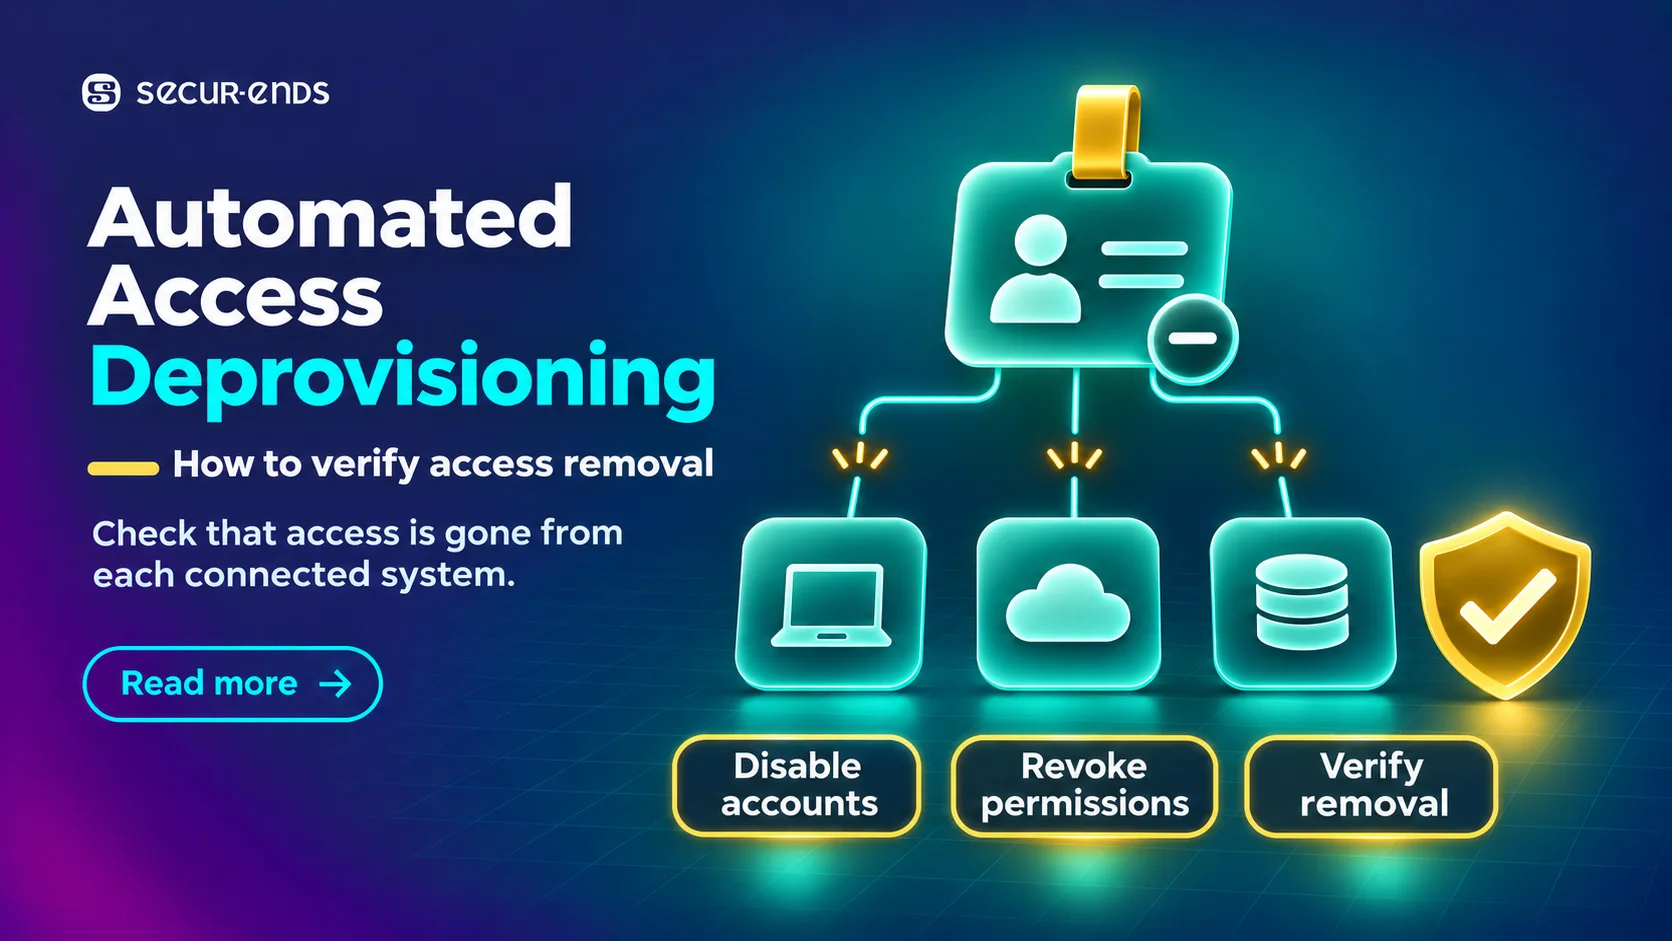
- Automated access deprovisioning removes or modifies permissions when employment, responsibilities, assignments, or access decisions change.
- Match each event to the correct identity, accounts, and entitlements before making changes.
- Track submitted requests, reported completion, and verified results separately.
- Keep failed or unmatched actions visible, with an owner and a defined path to resolution.
- Check for inherited permissions and governing assignments that may preserve or restore access.
When Offboarding Closes but Banking Access Remains Active
A bank’s HR system records an employee’s departure at 6 PM. An automated workflow disables the employee’s directory account and marks offboarding complete.
The next morning, IT finds that the former employee still has a local account in the loan origination platform. A privileged reporting account also remains active because it was never linked to the central identity. Automated access deprovisioning helps banks and credit unions address gaps like these by tracking each required change through verification in the affected system.
What Is Automated Access Deprovisioning?
Automated access deprovisioning is the use of defined events, policies, and integrations to remove or modify identity permissions when the underlying business authorisation changes or ends.
Triggers can include departures, transfers, expired assignments, rejected access certifications, and the end of privileged duties. The resulting action may disable an account, revoke a role, remove a group membership, or end temporary access. A departing employee’s interactive access may need to end while records remain subject to retention policies. An employee transferring departments may only need permissions from the previous role removed.
How to Define a Successful Deprovisioning Workflow
Each workflow stage establishes a different part of the outcome.
| Workflow stage | What it establishes | What still needs verification |
| Trigger received | The system received an event | Whether the event is valid and complete |
| Identity resolved | The workflow matched an identity | Whether all relevant accounts were identified |
| Removal requested | The workflow submitted a change | Whether the target system accepted it |
| Fulfilment reported | A connector or task reported completion | Whether the intended permission changed |
| Source state verified | The target system reflects the expected change | Whether another access path preserves the capability |
| Reconciliation confirmed | The access state remains consistent with policy at reconciliation | Whether later assignments change that state |
Match verification to the risk and the control being tested. An authoritative connector response may be sufficient for lower-risk access under the institution’s approved procedures. Sensitive permissions may require source-system reconciliation or additional authorised testing.
Which Access Paths Should Banks Check?
An employee may have several accounts or receive equivalent permissions through different assignments. Check the access paths affected by the business event.
| Access path | Example | Removal consideration |
| Central directory account | Employee network identity | Disabling it may affect connected applications |
| Application-specific account | Local loan origination account | May require separate deactivation |
| Directory group | Group granting financial report access | Remove the relevant membership |
| Application role | Lending approval authority | Revoke the correct role assignment |
| Privileged identity | Separate administrator account | Follow elevated-access removal procedures |
| Temporary permission | Approved production support role | Remove or expire the assignment |
| Existing session | Authenticated application session | Evaluate session or token invalidation where required |
How to Move From a Lifecycle Event to Verified Removal
- Validate the trigger. Confirm the authoritative source, affected identity, and effective date or time. Account for delayed, corrected, or cancelled events.
- Resolve the affected accounts and permissions. Determine whether the event calls for offboarding, selective removal, or another change. Flag unmatched accounts for investigation.
- Execute the approved change. Identify the exact account, entitlement, and target system. Use a supported connector or assign the change to an authorised administrator.
- Handle failures. Assign an owner, limit retries to suitable conditions, and escalate persistent errors.
- Verify the final state. Confirm the outcome using an updated entitlement report, reliable source-system response, reconciliation, or authorised testing.
How Removal Rules Vary by Lifecycle Event
| Trigger | Appropriate action | What to check |
| Employee termination | End the person’s access across relevant systems | Independent accounts are identified and addressed |
| Department transfer | Remove permissions tied to previous responsibilities | The employee retains access needed for current duties |
| Privileged assignment ends | Remove the additional authority | Any retained elevated access has current approval |
| Access review rejection | Revoke or modify the specific entitlement | The change targets the permission the reviewer rejected |
| Temporary role expires | End the approved temporary access | Any extension is authorised and recorded |
| Contractor assignment ends | Remove assignment-related access | Operational integrations are assessed separately |
| Security incident response | Apply approved containment and revocation actions | Urgent actions follow the required response timeline |
Use the approved effective time and system criticality to sequence changes. For example, a temporary deployment role should end when the authorised work finishes.
How a Bank Can Resolve Two Gaps in a Completed Workflow
A hypothetical community bank disables a departing employee’s central account, and the dashboard reports successful offboarding. Reconciliation exposes two unresolved actions:
- Unmatched lending account. The employee’s local loan origination username differs from their directory username. IT verifies ownership, removes the access, and updates the identity mapping.
- Failed reporting deactivation. The workflow finds the reporting account, but the connector receives an authorisation error. The bank assigns the failure to the integration owner and completes the removal through an approved process.
The bank checks updated records in both applications and reviews prior departures for similar mapping or connector failures. It also updates the dashboard so unresolved application actions stay visible when the central account has already been disabled.
Why Access Can Remain or Return After Removal
A user may receive reporting access through both a direct grant and a role. Removing the direct grant leaves the capability in place if the role still provides it. Depending on the platform and configuration, an active policy may also restore an entitlement during reconciliation.
Identify the role, group, policy, or request that governs the entitlement. Confirm whether the decision calls for removing one assignment or ending the user’s ability to perform a sensitive action. Reconcile again after important changes to check for restored or overlapping access.
How to Recover From Failed Removals
| Failure condition | Appropriate response | Evidence of resolution |
| Temporary API outage | Retry within supported limits | Successful action and confirmed state |
| Invalid connector credentials | Escalate to the integration owner | Connection corrected and change completed |
| Target account cannot be matched | Investigate identity correlation | Correct account identified and addressed |
| Another role governs the permission | Identify and update the governing assignment as authorised | Approved state persists after reconciliation |
| Manual fulfilment is required | Assign an accountable administrator | Change verified in the target system |
| Session remains active after disablement | Apply relevant session controls if required | Session invalidation or expiry evidence |
| Critical technical dependency | Follow an approved transition or risk treatment process | Documented final state and applicable safeguards |
Define when retries stop and escalation begins. Check that repeated attempts do not create duplicate or conflicting changes.
How to Evaluate Automated Access Deprovisioning Software
Ask vendors to demonstrate the path from an approved event to a confirmed application change. Establish whether each application supports direct removal, a ticketed process, or manual fulfilment.
| Evaluation area | Buyer question |
| Event sources | Can the platform receive reliable HR, certification, and access-change triggers? |
| Identity matching | Can it link users to local, privileged, and other relevant accounts? |
| Permission precision | Can it remove a specific entitlement while preserving authorised access? |
| Connector coverage | Which applications support direct changes? |
| Manual fulfilment | How are unsupported applications handled? |
| Error recovery | How are failures detected, retried, and escalated? |
| State verification | What evidence shows the target permission changed? |
| Reconciliation | Can the platform detect permissions that remain or return? |
| Historical evidence | Can earlier decisions and corrective actions be reconstructed? |
| Operational visibility | Are unresolved and high-risk actions visible? |
Six Proof-of-Concept Tests for Banking Teams
| Test case | Expected result |
| Employee termination across applications | Relevant accounts are identified, and required actions are completed or tracked as exceptions |
| Department transfer | Outdated permissions are removed while valid access continues |
| Failed connector operation | The error is visible, assigned, escalated, and resolved |
| Unmatched local banking account | The account or coverage gap is flagged for investigation |
| Overlapping or inherited entitlement | The governing assignment is addressed and effective access is verified |
| Immediate high-risk revocation | The action starts promptly and the target-system outcome is tracked |
Also test a duplicate event and an application outage. Check whether the workflow avoids conflicting changes and whether outstanding tasks are recovered or escalated once the application becomes available.
How to Measure Verified Access Removal
Consider a bank with 200 required removal actions during a review period.
| Outcome | Actions |
| Verified complete | 176 |
| Pending fulfilment | 14 |
| Failed and awaiting recovery | 10 |
| Total required actions | 200 |
The verified removal rate is 88%, with 176 of 200 actions confirmed. If the workflow initiated all 200 actions, the initiation rate would be 100%, while 24 actions would still lack verified completion.
| Metric | What it reveals |
| Required access paths identified | Identity and application coverage |
| Removal requests initiated | Workflow execution |
| Verified removals | Confirmed corrective outcomes |
| Actions pending or failed | Remaining operational exposure |
| Time from effective event to confirmed removal | End-to-end deprovisioning speed |
| Sensitive permissions exceeding internal targets | Delays affecting higher-risk access |
| Access restored unexpectedly after reconciliation | Potential assignment or policy errors |
Measure time from the authorised effective event to confirmed removal. Review overdue critical actions and longer delays alongside typical turnaround times so isolated but material delays remain visible.
Where Identity Governance Supports Deprovisioning
User access review workflows can help teams identify permissions for revocation and track the decisions that trigger corrective actions.
SecurEnds supports identity and entitlement visibility, access certification, and remediation workflows across connected applications. Its immediate revocation functionality can initiate removal through configured fulfilment methods. Completion depends on the target system and the process in place. Banks and credit unions should test connector coverage, manual fulfilment, exception tracking, and verification in their own environment. Identity Governance for Credit Unions
Best Practices for Automated Access Deprovisioning
- Use authoritative events and current effective dates. Validate corrections before changing access.
- Map the exact account and entitlement. Include local accounts, privileged identities, and inherited assignments.
- Assign and escalate failed actions. Keep each required removal open until the owner resolves or formally addresses it.
- Verify the resulting access state. Use evidence that matches the risk and covers relevant alternate access paths.
- Check that sensitive removals persist. Reconcile after the change to catch active policies or roles that restore access.
Frequently Asked Questions
What is automated access deprovisioning?
Automated access deprovisioning uses events, policies, and integrations to remove or modify permissions. It can disable accounts, remove roles, or revoke individual entitlements. A reliable process also detects failures and verifies the resulting access state.
Does disabling a central identity remove all banking application access?
Some applications maintain independent accounts or locally assigned permissions. Existing sessions may also need separate handling. Check which access paths depend on the central identity and verify changes in the affected systems.
What happens when a deprovisioning connector fails?
Keep the failed action visible and assign it to the appropriate owner. Temporary failures may allow controlled retries. Persistent failures may require investigation or manual fulfilment, followed by verification.
Can a removed entitlement reappear after identity reconciliation?
Yes, depending on the platform and configuration. An active role or policy may restore a permission. Identify the governing assignment, make the approved change, and confirm the result after reconciliation.
How is entitlement revocation different from account deactivation?
Entitlement revocation removes a specific permission, role, or assignment. Account deactivation prevents use of an account in the relevant system. Choose the action that matches the business event and intended restriction.
What evidence proves that automated deprovisioning succeeded?
Retain the original trigger, identity and entitlement mapping, removal request, fulfilment result, and evidence of the resulting access state. Sensitive or complex changes may require additional reconciliation or authorised testing.
What should banks look for in automated access deprovisioning software?
Check trigger reliability, identity matching, permission-level changes, connector coverage, failure handling, and verified removal reporting. Include local accounts, inherited permissions, duplicate events, and failed connectors in the pilot.
Make Access Removal a Verified Outcome
Start with a sensitive permission and test what happens when the first removal attempt fails. Confirm that the workflow identifies the right account and entitlement, assigns the issue to an owner, and captures evidence of the final state in the affected application. That gives the institution a way to measure whether the access it intended to remove actually ended.