API Access Governance: Managing Permissions in Banking
API Access Governance: Managing Permissions in Banking
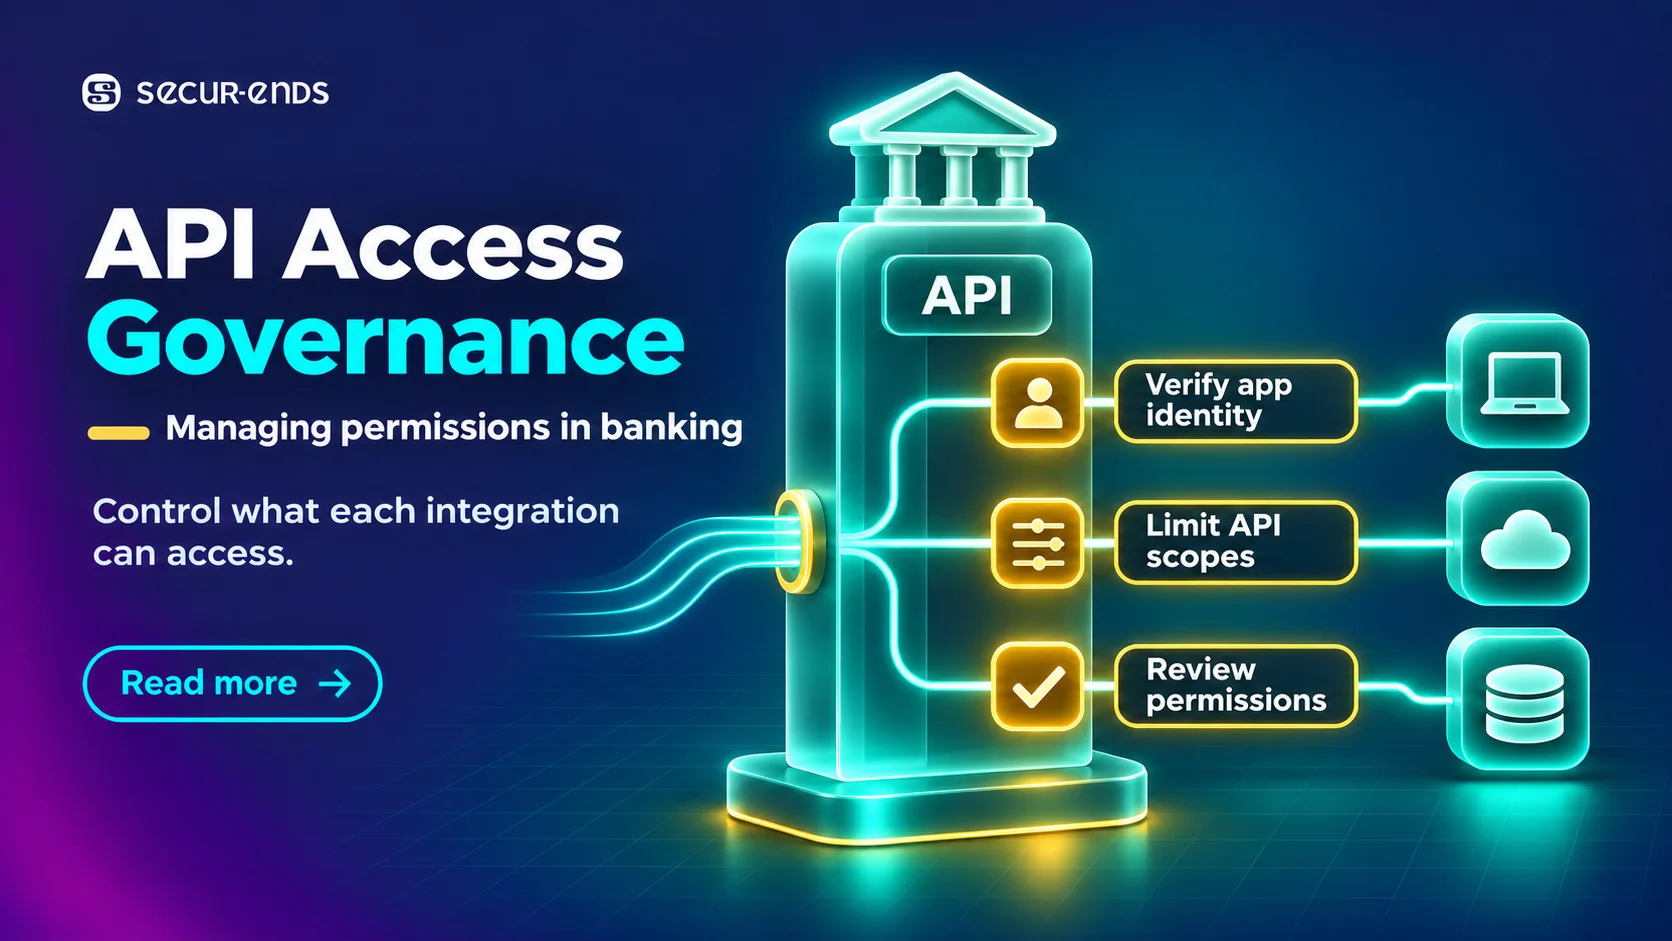
A credit union connects its loan origination platform to a reporting application through an API. During implementation, the reporting service receives permission to retrieve detailed borrower information.
The integration works as expected.
Six months later, the credit union changes its reporting process. The application now requires only loan status, product category and selected reporting fields. However, the API client still holds its original, broader permissions.
The connection remains authenticated. The requests may be technically valid. But the business justification for the original access has changed.
This is where API access governance becomes important.
Banks and credit unions depend on APIs to connect core systems, lending platforms, payment services, analytics tools and digital banking applications. Each integration can introduce identities, credentials and permissions that require continuing oversight.
The challenge is not only preventing unauthorised requests. It is establishing whether an integration should still possess the permissions that make those requests possible.
For financial institutions evaluating identity governance, that means connecting API access with accountable owners, legitimate business purposes, technical entitlements and verifiable access changes.
What Is API Access Governance?
API access governance is the process of establishing ownership, business justification, approval, review and lifecycle controls for identities and permissions used to access APIs.
It helps organisations determine which applications, services and workloads are authorised to use particular API capabilities.
In banking, an API client may support a loan reporting service, payment integration, fraud detection platform or customer-facing application.
The client can have technically valid credentials and still hold more access than its current business purpose requires.
API access governance provides a way to reassess that authority as systems and business requirements change.
However, governance should not be confused with the technical mechanisms that enforce API security.
API Authentication, Authorisation and Governance
| Control | Question it answers | Banking example |
| Authentication | Which client or identity is making the request? | A reporting service authenticates with approved credentials |
| Authorisation | Is the requested operation or resource permitted? | The API permits access to an authorised loan record |
| Access governance | Should the client continue holding that permission? | The lending owner confirms whether detailed loan access remains necessary |
All three are relevant, but they operate at different levels.
An API gateway or resource server may correctly enforce a configured policy even when that policy grants unnecessarily broad access.
Conversely, an access review may approve a legitimate business purpose without proving that the API’s technical authorisation checks are correctly implemented.
Institutions need to understand both distinctions.
Where API Permissions Exist Across Banking Operations
An API inventory can identify connections between applications, but it does not automatically show whether their permissions are appropriate.
Banks should connect their integration inventory with access ownership and authorisation information.
| Banking integration | Illustrative API access | Main governance concern |
| Loan origination and reporting | Read loan records | Excessive access to borrower details |
| Digital banking and core systems | Retrieve authorised account information | Improperly broad resource permissions |
| Payment platform | Submit or retrieve payment information | Unnecessary transaction-related authority |
| Fraud monitoring service | Retrieve approved transaction signals | Access extending beyond current monitoring needs |
| Customer analytics application | Read selected customer data | Continued access to unneeded information |
| Third-party banking provider | Perform agreed service operations | Unclear ownership or outdated permissions |
| Internal automation | Execute scheduled technical tasks | Persistent permissions without current justification |
These are examples rather than universal banking API configurations.
The exact permissions depend on the provider, API design, identity system and financial institution’s operating model.
A useful governance process should identify both the technical client and the business function responsible for its access.
Five Questions Every Banking API Client Should Answer
Before an institution can make an informed access decision, it needs enough information about the API client.
Five questions provide a practical starting point.
1. Which Identity Is Accessing the API?
Identify the registered client, service identity, workload identity or other principal making requests.
The record should distinguish the technical identity from the application name displayed in a dashboard.
One business service may use several clients, and one client may support multiple workflows.
That relationship matters when permissions are changed or revoked.
2. Which Business Service Requires the Access?
The client should be associated with an approved business purpose.
For example, a service may retrieve loan status information to produce a daily operational report.
A description such as production integration is not sufficient to explain why sensitive API permissions remain necessary.
3. Who Is Accountable for the Integration?
Assign a business owner who can confirm continuing need and a technical owner who understands the integration.
These may be different individuals.
The business owner establishes why access is required. The technical owner explains how permissions are configured and what changes could affect the application.
4. What Can the Client Actually Do?
Identify the scopes, roles, application permissions or other authorisation rules applicable to the client.
A scope name may describe a general permission without fully specifying which records or properties can be accessed.
The reviewer needs the technical context necessary to understand the actual authority.
5. When Must the Access Change or End?
Establish how access responds to service retirement, application replacement, changing data requirements and ownership transfers.
A client should not retain indefinite permission solely because it was approved during implementation.
These answers form the foundation for informed access reviews.
OAuth Scopes: Useful Permission Signals, but Not Complete Authorisation
OAuth is commonly used to support delegated or application access to APIs.
In OAuth-based systems, scopes can represent permissions requested or granted to a client.
For example, a financial API might define the following illustrative scopes.
| Illustrative scope | Possible capability | Access review question |
| loan.status.read | Read authorised loan status information | Does the service still require these records? |
| loan.details.read | Read detailed loan information | Is access to borrower-level data necessary? |
| payment.status.read | Retrieve permitted payment status | Which business process depends on it? |
| payment.initiate | Request an authorised payment operation | Is this client approved to initiate payments? |
| customer.profile.read | Retrieve permitted customer details | Is the data scope appropriate? |
These names are examples, not standard scopes that all banking APIs must implement.
Their meaning depends on the particular authorisation and resource server.
Why a Valid Scope Does Not Guarantee Appropriate Data Access
Consider an API client holding a scope that permits loan information retrieval.
The scope may establish permission to call a particular category of API operation.
However, the resource server still needs to determine which loan records the client can legitimately access.
If an application can retrieve another customer’s records by changing an object identifier, it may have an object-level authorisation weakness.
Similarly, an API may expose properties that should be restricted even though the client is authorised to access the overall object.
These are technical authorisation issues.
API access governance determines whether the client should possess a permission. API security controls must still enforce what that permission actually allows.
The two functions complement one another but are not substitutes.
Banking Scenario: Reducing an Overprivileged Reporting API
Consider a hypothetical community bank using an external analytics service for loan portfolio reporting.
During deployment, the service requires detailed borrower information to validate reporting accuracy.
The bank creates an API client and authorises broader read permissions for the implementation.
After the reports are established, the analytics service changes to a workflow that needs only approved loan status and aggregated reporting information.
The API client retains its original permissions.
Identify the Client and Its Current Authority
The integration team identifies the registered client, relevant scopes, authorised resources and technical service owner.
It also establishes whether the same client supports any other approved workflows.
Confirm the Changed Business Need
The lending analytics owner determines that the service no longer requires detailed borrower information.
The API owner translates that requirement into the appropriate technical authorisation changes.
This is not simply a credential maintenance activity. It is a change to the client’s authorised capabilities.
Check Whether the Client Is Shared
The bank discovers that the same API client is also used by a separate loan quality-control process.
That second workflow still requires certain information unavailable under the proposed restricted scope.
Immediately removing the broad permission could disrupt legitimate operations.
The institution evaluates whether the workflows should use separate client identities or another appropriate authorisation design.
Apply the Approved Change
The bank separates the access requirements where appropriate and updates the relevant client authorisation.
The analytics service receives the narrower permissions needed for its current function.
The quality-control process retains only the access justified for its own approved purpose.
Verify the Result
The technical team confirms that permitted reports continue to run.
It also checks, through appropriate negative authorisation tests, that the restricted analytics client cannot perform the operations or retrieve the information that should no longer be accessible.
The institution retains the decision, configuration change and relevant verification evidence.
Address the Underlying Process Gap
The bank establishes a review trigger for material changes in API data requirements.
Future changes to an integration’s business purpose will prompt reassessment of its permissions.
The governance improvement is not merely a smaller scope. It is a repeatable process for connecting technical authority with current business requirements.
Why Shared API Clients Complicate Access Governance
Some integrations use one technical client for several business services.
That design may simplify initial configuration but can make least-privilege access more difficult.
If two services require different permissions, a shared client may receive the combined authority.
Removing access for one service can disrupt the other.
For example, a reporting workflow may need read access while an operational integration requires limited write capabilities.
If both use the same client, reviewers cannot necessarily revoke one workflow’s access without affecting the other.
When Should Clients Be Separated?
Banks should consider separate client identities when workloads have materially different owners, permissions, environments or lifecycle requirements.
This is a design consideration, not a universal rule that every integration requires its own registered client.
The decision should reflect operational dependencies and the platform’s capabilities.
What Should the Review Capture?
Where clients are shared, the institution should document the relevant services, owners and dependencies.
An access review should not assume that one application name represents one business purpose.
These relationships become particularly important during scope reduction and retirement.
Token Security and Access Governance Solve Different Problems
API security discussions frequently focus on credential rotation, token lifetimes and secure authentication.
Those controls are important, but they do not independently establish appropriate business authorisation.
| Technical control | What it helps protect | What governance must still establish |
| Client secret rotation | Credential lifecycle and exposure risk | Whether the client’s permissions remain justified |
| Short-lived access token | Duration of an issued token | Whether the client can obtain new authorised tokens |
| Audience-restricted token | Where a token is intended to be accepted | Whether access to that API is appropriate |
| Sender-constrained token | Misuse of certain stolen tokens | Whether the underlying authorisation is necessary |
| Scope reduction | Limits an identified permission | Whether other grants preserve equivalent authority |
| Client retirement | Ends an unnecessary integration identity | Whether all related credentials and dependencies are addressed |
The OAuth 2.0 Security Best Current Practice describes technical protections such as audience restriction and sender-constrained tokens.
These measures improve token security.
They do not determine whether an analytics application should continue to retrieve detailed borrower data.
That remains an access governance decision supported by the bank’s business and technical owners.
The API Access Lifecycle: From Approval to Retirement
A banking integration should be governed throughout its useful life.
Permissions approved during implementation may become inappropriate when the service changes.
New Integration
Establish the service’s purpose, accountable owners, required APIs, permission scope and intended operating conditions.
Approvals should identify the authority actually needed.
Expansion
When a service requires new operations or data, evaluate the incremental permissions.
The existence of an approved API connection does not automatically justify granting every additional scope.
Business Requirement Change
When the workflow changes, determine whether the existing permissions remain appropriate.
A service that no longer processes borrower details should not automatically retain broad borrower-data access.
Ownership Transfer
If a business or technical owner leaves, the institution should reassign accountability and investigate unresolved permissions.
A working integration should not be treated as properly governed if no responsible owner can explain its purpose.
Retirement
When the business service ends, identify the relevant client registrations, credentials, permissions and dependencies.
The technical team should establish whether other workflows still rely on the same identity.
Required access changes should be executed and verified through an approved process.
The institution should preserve appropriate historical evidence according to its records policies.
How to Review API Permissions Without Disrupting Banking Services
An API access review should provide more than a list of client IDs and scope strings.
The reviewer needs sufficient business and technical context to distinguish necessary access from excessive authority.
| Reviewer information | Why it matters |
| API client identifier | Establishes which technical identity is being reviewed |
| Business service | Explains the legitimate purpose |
| Business and technical owners | Establishes decision accountability |
| Resource or API | Identifies where the client has access |
| Granted scopes or roles | Describes the assigned capabilities |
| Relevant dependencies | Identifies services affected by removal |
| Review decision | Records whether access should remain or change |
| Remediation evidence | Demonstrates what happened after the decision |
A reviewer may decide to retain, reduce, investigate or retire access.
For sensitive permissions, the review may require information from both the business owner and API owner.
Usage Data Is Helpful, but It Is Not the Final Decision
An API client that has not made a request recently may deserve investigation.
However, some legitimate integrations operate monthly, quarterly or only during specific events.
Inactivity alone does not always justify immediate deletion.
Similarly, frequent usage does not prove that every granted permission is necessary.
Usage should inform the review, not replace business authorisation.
What Happens When an API Client Has No Owner?
An orphaned API client is a technical identity without clear current accountability.
It may still be exchanging information with banking systems.
Immediately disabling it without investigating dependencies could interrupt important operations.
Leaving it active indefinitely also creates an unacceptable governance uncertainty.
The institution should investigate the client registration, authorised resources, usage patterns, connected workload and original business purpose.
Where the integration remains necessary, an appropriate owner should be assigned and the permissions reviewed.
Where the service is no longer required, the institution should follow an approved retirement process.
If the business purpose cannot be established, the issue should be escalated according to the institution’s risk procedures.
The key is to make the ownership gap visible and actionable.
What API Access Governance Software Should Actually Do
For banks and credit unions evaluating software, the important question is whether the product can turn technical API identity information into useful governance decisions.
A platform may discover service accounts without collecting their actual API permissions.
Another may provide detailed OAuth scope information without supporting business-owner certification.
The buyer should establish which capabilities are native, integrated or dependent on manual processes.
| Evaluation capability | Questions for the vendor |
| API identity discovery | Can the product identify relevant API clients and service identities? |
| Ownership mapping | Can technical identities be linked to accountable business and technical owners? |
| Scope and role visibility | Can granted permissions be collected or reliably represented? |
| Business context | Can a reviewer understand the integration’s actual purpose? |
| Shared-client relationships | Can multiple services using one client be identified or documented? |
| Access certification | Can owners reassess the continuing business need? |
| Change tracking | Can permission decisions be connected to implementation tasks? |
| Remediation verification | Can the intended scope or role change be confirmed? |
| Orphan identification | Are clients without accountable owners surfaced? |
| Lifecycle events | Can integration changes or retirement trigger governance actions? |
| Historical evidence | Can previous access decisions and outcomes be reconstructed? |
Clarify the Product Boundary
An identity governance solution may support access ownership, certification and remediation workflows.
It does not automatically replace an API gateway, authorisation server, secrets manager or application security testing platform.
For example, a governance product may establish that a client should no longer hold a broad scope.
The authorisation infrastructure must still implement the change, and the resource server must correctly enforce access to individual resources.
Buyers should understand how those responsibilities are divided.
Six API Governance Proof-of-Concept Tests
A practical software evaluation should use realistic banking integrations rather than only a generic service-account inventory.
| Test | Scenario | Expected outcome |
| 1 | New loan reporting integration | Client identity, owner, purpose and permissions are documented |
| 2 | Reporting service no longer needs detailed borrower data | Excess scopes are identified and a reduction is tracked |
| 3 | One API client supports multiple approved services | Shared dependencies are visible before changes |
| 4 | Business owner leaves the institution | Ownership gap triggers reassignment or escalation |
| 5 | An integration is retired | Related access changes are coordinated and verified |
| 6 | The client retains access through another grant | Review identifies that the intended restriction may not be effective |
The second test is particularly valuable.
Ask the vendor to demonstrate the complete record: the original scope, the business decision to reduce access, the technical action and evidence of the new permission state.
Where the platform cannot execute a change directly, it should accurately represent the outstanding fulfillment process.
A successful pilot should not confuse a completed review with a completed authorisation change.
How to Measure API Access Governance Effectiveness
Counting registered API clients can help establish inventory scale, but it is not sufficient to assess governance quality.
For example, consider a hypothetical bank with 120 identified API clients.
Of those, 102 have confirmed accountable owners.
<text>Ownership coverage: 102 ÷ 120 × 100 = 85%.</text>
Eighteen clients require ownership investigation.
This is useful information, but it does not establish whether the 102 owned clients hold appropriate scopes.
The bank should also assess the quality of permissions and lifecycle actions.
| Metric | What it helps establish |
| API clients linked to valid owners | Accountability |
| Clients mapped to active business services | Continuing justification |
| Sensitive API permissions within review scope | Governance coverage |
| Unowned API clients | Ownership gaps |
| Shared clients with unclear dependencies | Change-management risk |
| Permission reductions verified complete | Remediation effectiveness |
| Retired services with active clients or grants | Incomplete decommissioning |
| Clients outside governance data collection | Visibility limitations |
For high-impact integrations, the institution may also track how long unnecessary permissions remain active after an approved removal decision.
These measures should be interpreted in the context of the organisation’s technology environment and risk assessment.
How Identity Governance Supports API Access Reviews
API permissions may be distributed across identity providers, authorisation servers, cloud platforms and business applications.
Identity governance can help organise available account and entitlement information and associate it with accountable reviewers.
For financial institutions using user access review workflows, relevant API clients and service identities may be included where supported integrations provide sufficient visibility.
The institution should verify whether the information presented to reviewers accurately represents the permissions being evaluated.
A certification decision is useful governance evidence, but it does not independently prove that every API enforces correct object-level or function-level authorisation.
Where SecurEnds Fits Into Banking API Governance
SecurEnds positions its identity governance capabilities around visibility, ownership, access certification and remediation across connected identities and applications, including non-human identity use cases.
These capabilities can support API-related governance where the institution can collect the relevant client or service-account information and associate it with permissions.
For credit unions managing technical identities alongside employee and vendor access, the identity governance framework for credit unions provides broader context for access oversight.
During evaluation, banks should confirm the specific API identity sources, scope visibility, integration methods and remediation capabilities supported in their environment.
No identity governance product should be assumed to provide complete API security testing or universal scope enforcement without verifying those functions.
Conclusion: Match API Permissions to the Current Business Need
APIs allow banks and credit unions to connect essential systems, automate workflows and support digital financial services.
However, an integration that works correctly may still possess more authority than it needs.
API access governance helps institutions identify the clients accessing their services, understand the permissions those clients hold and connect that authority to accountable business owners.
It also provides a process for reassessing access when reporting needs change, integrations expand, ownership transfers or services are retired.
For banks evaluating governance software, start with one API client whose permissions have changed since implementation.
Can the institution explain the original approval, identify the current business need, assess shared dependencies, implement the correct reduction and verify the result?
Effective API access governance ensures that machine-to-machine permissions remain justified, controlled and traceable—not merely technically valid.
Frequently Asked Questions
1. What is API access governance?
API access governance manages the ownership, business justification, permissions, review decisions and lifecycle of identities authorised to use APIs. These may include applications, service accounts and workload identities. For banks, the objective is to ensure that integrations retain only the authority appropriate to their current business purpose.
2. How is API access governance different from API access management?
API access management typically concerns technical controls such as authentication, tokens, scopes and authorisation policies. API access governance concerns who is accountable for client permissions, whether those permissions remain necessary and how changes are approved and tracked. Governance supports technical enforcement but does not replace it.
3. Why should banks review OAuth scopes?
OAuth scopes can represent permissions granted to API clients. An integration may no longer need access that was authorised during implementation. Reviewing scopes helps identify potentially excessive permissions. However, scope approval alone does not prove that the API correctly enforces object-level, property-level or function-level authorisation.
4. Does rotating API credentials reduce excessive permissions?
Credential rotation helps maintain the security of authentication material but does not necessarily change the client’s authorisations. A newly issued credential may still provide access to the same scopes or resources. Banks should evaluate credential security separately from whether the client retains permissions appropriate to its current business requirements.
5. How should banks manage API clients without an identified owner?
Banks should investigate the client registration, connected application, permissions, observed activity and service dependencies. If the integration remains necessary, an accountable owner should be assigned and access reassessed. If it is obsolete, the institution should follow a controlled retirement process that avoids unintended disruption to critical banking services.
6. Can identity governance software prevent broken API authorisation?
Not by itself. Identity governance can support client ownership, permission reviews and access lifecycle decisions. Broken object-level or function-level authorisation involves technical enforcement within API systems and requires appropriate application design and testing. Banks should evaluate governance alongside API security, token protection and authorisation controls.
7. What should banks look for in API access governance software?
Banks should assess API client visibility, owner mapping, scope and entitlement information, business context, access certification, lifecycle workflows, remediation tracking and historical evidence. They should also confirm support for the institution’s actual API platforms. A strong evaluation demonstrates a permission reduction from business approval through verified technical implementation.