Banking Entitlement Management for Better Access Decisions
Banking Entitlement Management for Better Access Decisions
TL;DR
- Banking entitlement management helps institutions understand what permissions allow, who holds them, and whether they are still needed.
- Review the permissions behind each role, including direct assignments and access inherited through groups.
- Start the entitlement catalog with sensitive permissions. Validate what each permission allows and assign an accountable owner.
- Test software against actual banking systems, from entitlement collection through verified remediation.
- Track unresolved exceptions and confirmed access changes alongside certification completion.
When Permission Codes Leave Reviewers Guessing
A credit union manager receives an access review for a lending employee. The report lists LN_APR_L2, CORE_MAINT_SUP, and BR_RPT_ALL. The manager knows the employee’s responsibilities but cannot tell which codes allow reporting, loan approvals, or sensitive account changes.
Banking entitlement management gives reviewers the context they need to decide which permissions still match the employee’s duties.
What Is Banking Entitlement Management?
Banking entitlement management is the process of defining, assigning, tracking, reviewing, and removing permissions that govern activities within financial applications and systems.
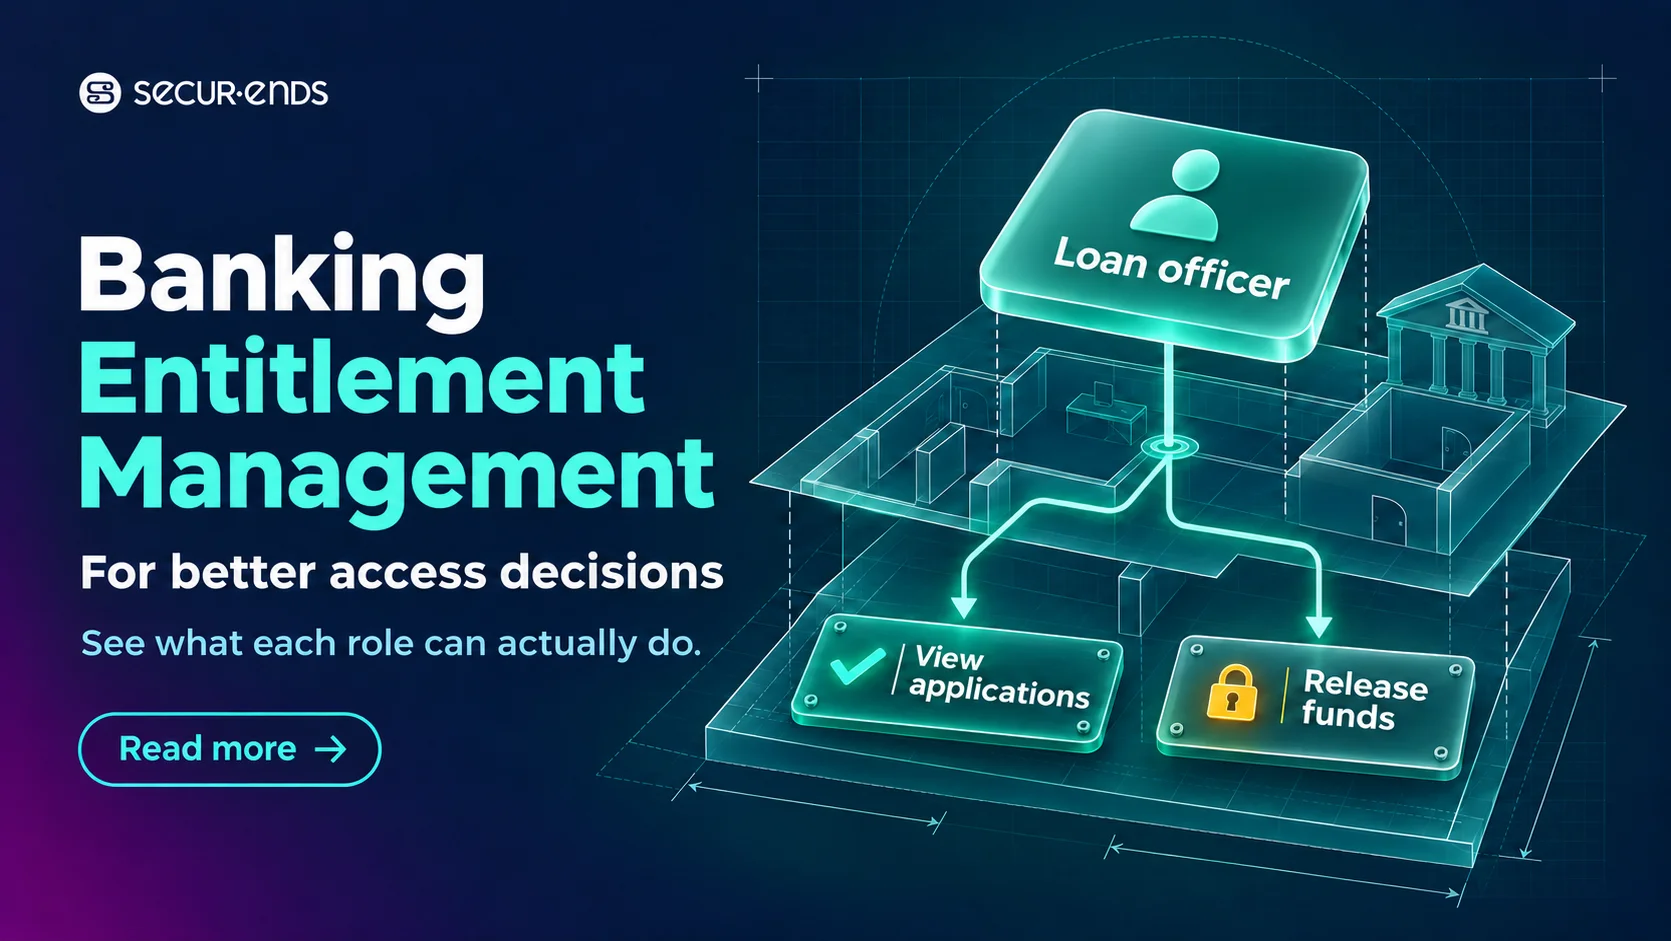
A user account identifies someone within an application. An entitlement specifies what that account can do. A teller and a supervisor may both use the same core banking platform, while only the supervisor can perform certain account maintenance activities.
The distinction matters when access is spread across core banking, loan origination, payments, reporting, and Active Directory. One employee may hold several accounts and receive permissions through direct assignments, inherited groups, and application roles.
When a Role Name Does Not Tell the Full Story
A role called “Lending Supervisor” might include loan approvals, reporting, and application maintenance. Another platform might use the same role name for a different set of permissions. Reviewers need to decide whether the employee still needs the role and whether the underlying permissions match their responsibilities.
Translating Technical Permissions Into Business Meaning
| Technical entitlement | Business meaning | Accountable owner |
| LN_APR_L2 | Approve eligible loans within defined authority | Lending operations |
| CORE_MAINT_SUP | Perform authorised supervisory account maintenance | Core banking owner |
| BR_RPT_ALL | Access approved branch operational reports | Branch operations |
| PAY_REL_AUTH | Authorise eligible payment releases | Payments operations |
| USR_ADMIN | Create or modify application user accounts | IT application administration |
These fictional codes show how descriptions and ownership can help managers review access. Validate each description against the application configuration before using it in certification.
Four Problems an Entitlement Management Solution Must Solve
Unclear Permission Ownership
IT may administer a loan approval entitlement, while lending management decides which employees should hold it. Assign sensitive permissions to owners who understand the business purpose and can authorise changes.
Fragmented Identity Records
An employee may use different identifiers in core banking and lending applications and receive additional access through directory groups. Reconcile those accounts to the correct employee, contractor, or technical owner so reviewers can assess the person’s combined access.
Outdated Permission Assignments
A loan processor who becomes an underwriter may retain permissions from the former role. Reassess access when responsibilities change, alongside scheduled certification campaigns.
Incomplete Remediation
A reviewer’s decision to revoke access may trigger an automated update, a service-management ticket, or a manual application change. Track the action through completion and confirm the result in the affected system.
What a Trustworthy Banking Entitlement Catalog Looks Like
An entitlement catalog records what permissions exist, what they allow, and who is responsible for them.
| Catalog attribute | Why it matters |
| Application and entitlement ID | Identifies the exact permission being governed |
| Business description | Explains what the permission enables |
| Business owner | Establishes approval responsibility |
| Technical owner | Identifies who maintains the permission |
| Risk classification | Highlights sensitive or elevated authority |
| Eligible business roles | Connects permissions with approved job functions |
| Assignment method | Identifies direct, group-based, or role-derived access |
| Review requirements | Establishes appropriate certification expectations |
| Last validation date | Indicates when the description and ownership were checked |
Which Entitlements Should Be Cataloged First?
Start with permissions for loan approval, payment authorisation, account maintenance, privileged administration, confidential member information, and changes to critical configurations. Recheck descriptions and risk classifications after system upgrades, and confirm ownership after departmental changes.
How a Credit Union Can Turn Unclear Permissions Into Defensible Decisions
A hypothetical credit union exports records from its lending and core banking applications. IT finds technical permissions with unclear descriptions, accounts it cannot match to employees, and sensitive entitlements with no documented business owner.
- Reconcile the accounts. Match application accounts to employee and contractor records. Flag unmatched accounts and assign technical or application owners to service accounts.
- Validate the permissions. Work with application specialists and business teams to confirm what sensitive entitlements allow and which restrictions apply.
- Assign business owners. Lending management takes responsibility for loan approval permissions, core banking operations owns specified maintenance entitlements, and IT implements approved changes.
- Review and correct access. When an employee transfers to branch operations, the lending owner confirms that an inherited lending entitlement is no longer needed. IT removes it and retains evidence of the updated access alongside the original entitlement and review decision.
How to Evaluate Banking Entitlement Management Software
Ask vendors to demonstrate how the platform works with your applications, permission structures, and review processes.
| Evaluation area | What to verify |
| Application connectivity | Can it collect entitlement-level data from the required systems? |
| Identity correlation | Can accounts be matched to employees and accountable owners? |
| Entitlement visibility | Can users view direct, inherited, and role-based permissions where supported? |
| Business context | Can accurate descriptions, owners, and risk information be maintained? |
| Access certification | Can reviewers assess permissions with enough information to make decisions? |
| Remediation | Can revocations be initiated or tracked through approved workflows? |
| Audit evidence | Are decisions, exceptions, and completed changes traceable? |
| Operational fit | Can the solution support both modern and legacy banking environments? |
Why Integration Depth Matters
One connector may import account records, while another can collect detailed entitlements but requires manual revocation. Ask vendors to show which permissions, roles, and group memberships each integration can retrieve and how changes are applied. Legacy systems may require controlled exports or other supported methods.
A Practical Proof of Concept for Entitlement Governance
Select one core banking platform and one connected system, such as a lending application or identity directory. Include an employee with standard access, one with inherited access, and an account whose ownership needs investigation.
- Collect the relevant accounts and entitlements.
- Correlate accounts with identities or accountable owners.
- Explain permissions using validated descriptions.
- Route sensitive decisions to accountable reviewers.
- Remediate inappropriate access through the approved workflow.
- Verify the change and preserve the supporting evidence.
Record where the process requires manual intervention so the institution can evaluate the operational work involved.
How to Measure Pilot Success
| Pilot measure | What it helps establish |
| Account reconciliation coverage | Whether accounts can be associated with the correct identities |
| Validated entitlement descriptions | Whether permission data is understandable and accurate |
| Sensitive entitlements with owners | Whether approval accountability is established |
| Unresolved access exceptions | Whether material problems remain visible |
| Verified revocations | Whether corrective actions were implemented |
| Repeated data-quality issues | Whether source information needs improvement |
Interpret the measures in context. A high account-matching rate can still leave a material gap if the unmatched accounts hold broad administrative permissions.
How Access Certification Strengthens Entitlement Management
The catalog explains what a permission allows. Access certification establishes whether a specific identity should still hold it. Clear descriptions help managers make decisions, and certification can reveal outdated assignments or catalog entries that need correction.
For institutions reviewing permissions across several systems, automated user access reviews can help coordinate decisions, track remediation, and retain evidence.
What Banks and Credit Unions Should Be Able to Demonstrate
NCUA examination guidance addresses access based on job responsibilities, supervisory controls, and independent reviews. A maintained catalog can support the audit record alongside approval decisions, application controls, and evidence of completed changes.
For sensitive entitlements, retain:
- The identity, application, and permission reviewed.
- What the permission allowed and who owned the decision.
- Why access was retained or removed and whether any exception remains open.
- How the institution verified the corrective action.
Where Entitlement Governance Fits Into Credit Union Identity Strategy
Hiring, transfers, contractor departures, and continuing service-account access all affect permissions across banking applications. SecurEnds provides identity and entitlement mapping, user-to-entitlement visibility, access certification workflows, and audit reporting. Evaluate these capabilities against your integrations, data quality, ownership model, and remediation requirements. Identity Governance for Credit Unions
Best Practices for Banking Entitlement Management
- Catalog sensitive permissions first. Start with access that affects lending decisions, payments, member records, and system administration.
- Validate descriptions against the application. Confirm what each entitlement allows and which restrictions apply.
- Separate business ownership from technical administration. Give approval decisions to owners who understand the business risk and assign changes to the teams that can implement them.
- Reassess access when responsibilities change. Review inherited and direct permissions after transfers and departures.
- Verify revocations in the affected system. Keep the original entitlement, approved decision, change record, and evidence of the updated access together.
Frequently Asked Questions
How is banking entitlement management different from role-based access control?
Role-based access control groups permissions by job responsibility. Entitlement management governs the underlying permissions, including those assigned directly or inherited through multiple roles, and tracks how they are reviewed and removed.
Why do banks need business-readable entitlement descriptions?
Clear descriptions help managers understand what technical permissions allow and decide whether access still matches an employee’s responsibilities. Application owners should validate descriptions against the actual configuration.
Can banking entitlement management software govern legacy core banking applications?
It may be possible through supported connectors, controlled exports, or other integration methods. Verify what entitlement detail the solution can collect, how it matches accounts to identities, and how access changes are implemented.
Who should own entitlements in a credit union?
Assign ownership to people who understand the permission’s purpose and risk. Lending management may own loan approval authority, for example, while IT administers the application and implements approved changes.
How can banks identify entitlements that employees no longer need?
Compare current permissions with authorised responsibilities after transfers, departures, or unusual assignments. Review what the access actually allows, then verify approved removals in the affected systems.
What should banks verify before purchasing banking entitlement management software?
Test integration depth, entitlement data quality, identity reconciliation, reviewer context, remediation options, and audit reporting. Use actual banking applications in the proof of concept.
How can credit unions measure whether entitlement governance is improving?
Track verified account ownership, validated descriptions for sensitive permissions, unresolved exceptions, overdue revocations, and confirmed remediation. Assess these measures alongside the risk of the remaining findings.
Better Access Decisions Begin With Better Entitlement Data
Start with a sensitive banking permission and follow it from its technical identifier to its business owner, review decision, and verified outcome. That gives banks and credit unions a practical way to assess whether their entitlement data supports defensible decisions across systems.