Sensitive Data Access Management: Who Can See Member Data?
Sensitive Data Access Management: Who Can See Member Data?
TL;DR
- Sensitive data access management establishes who can reach confidential information and what they can do with it.
- Review access beyond core banking, including shared folders, lending repositories, reporting platforms, and connected systems.
- Prioritise permissions by data sensitivity, access scope, permitted actions, and current business need.
- Use a pilot repository to test whether a solution can identify effective access, route decisions to owners, and verify changes.
- Combine identity governance with data discovery, classification, monitoring, and enforcement controls.
When Lending Access Ends but the Documents Stay Visible
A credit union employee transfers from lending to branch operations. Their loan origination access is removed, but they can still open a shared folder containing borrower income statements, credit reports, and identity documents.
The folder permissions were never updated. Sensitive data access management helps banks and credit unions find gaps like this across the locations where confidential information is stored, copied, or shared.
What Is Sensitive Data Access Management?
Sensitive data access management is the process of identifying, controlling, reviewing, and maintaining permissions that determine who can access confidential or regulated information.
For banks and credit unions, that includes member records, customer financial information, lending documents, and payment details. A review connects three elements:
- Data sensitivity determines what information needs protection and where it resides.
- Identity and ownership establish which employees, contractors, applications, or service accounts can reach the information and who is accountable for their access.
- Effective permissions show whether those identities can view, modify, export, share, or delete the data.
Where Sensitive Data Can Be Exposed Outside Core Banking
Financial information can move from its original application into reports, shared repositories, analytics platforms, and approved third-party workflows. Each location can have its own permissions.
Member Records in Reports and Exports
An employee may need account information to serve members at one branch. Review whether the same employee can access identifiable records across the institution through reporting tools or bulk exports.
Lending Documents in Shared Repositories
Shared lending folders can contain income statements, identification documents, and credit reports. When employees transfer, review the folder permissions alongside their loan origination access.
Customer Information in Analytics Platforms
Analytics platforms may combine information from core banking, lending, and payments. Check whether aggregated or appropriately de-identified reports can meet the business need before granting access to customer-level data.
Third-Party and Technical Access
Give service providers, contractors, and integrations a documented business purpose, accountable owner, and appropriately restricted access. Confirm operational dependencies before changing a service account that supports an active integration.
Which Sensitive Data Permissions Should Banks Investigate First?
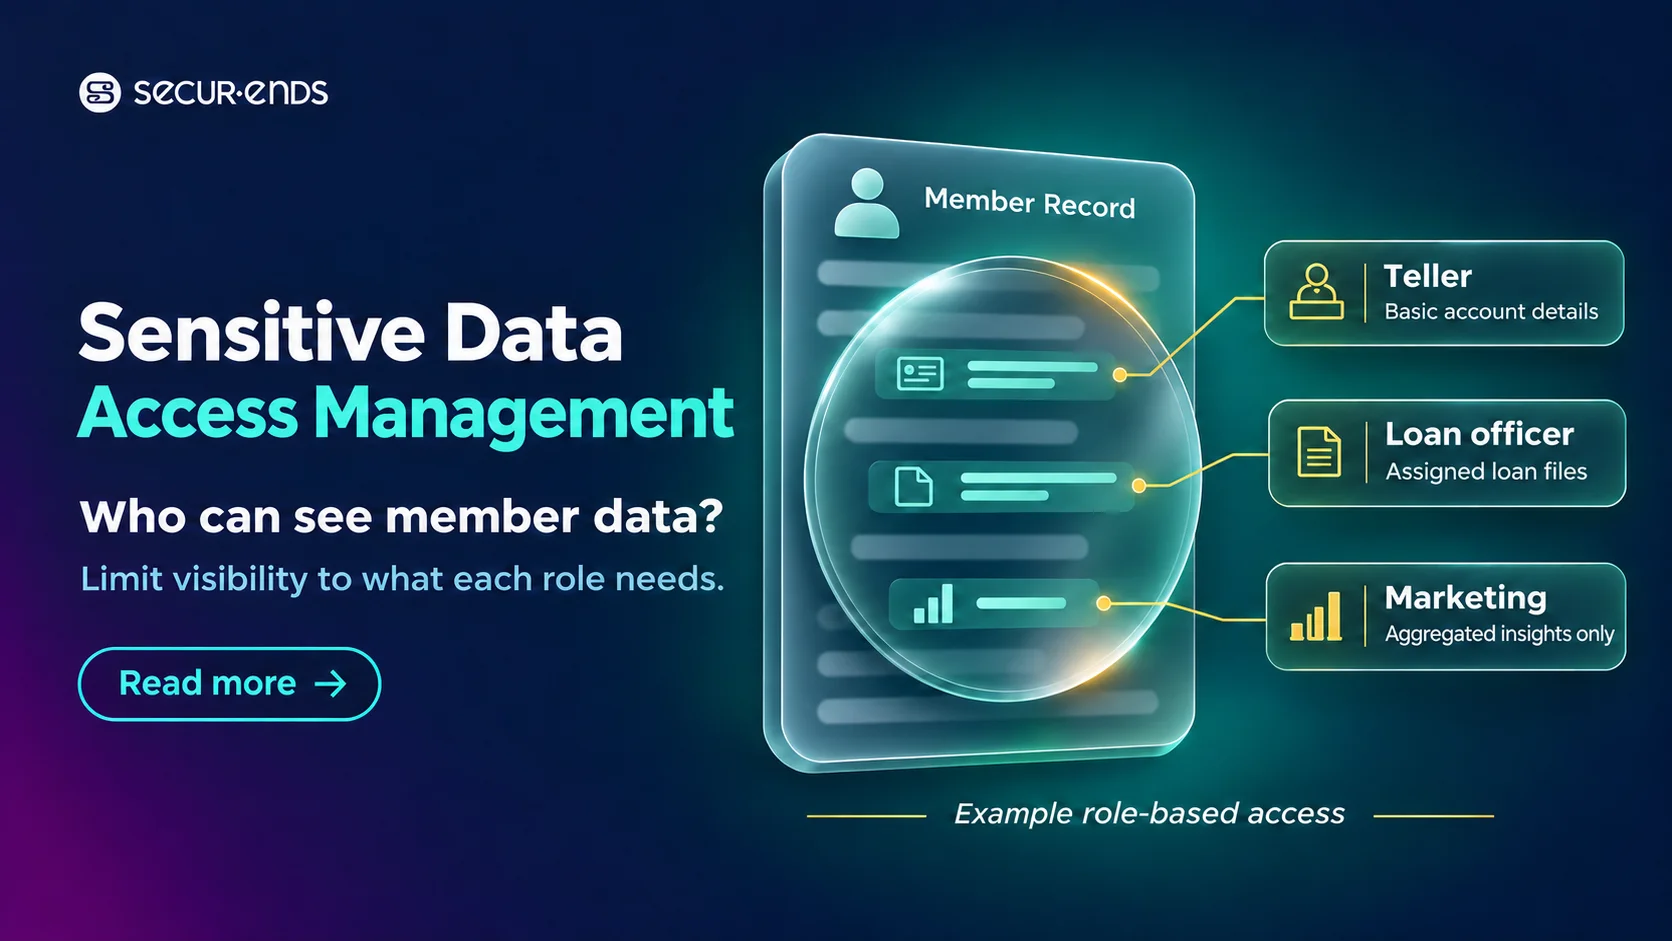
Prioritise permissions based on four questions. How sensitive is the information? How much can the identity reach? What actions can it perform? Is there a current business justification and an accountable owner?
| Data environment | Potential exposure | Priority consideration | Control to evaluate |
| Core banking | Broad access to member financial records | High when access exceeds assigned responsibilities | Scope permissions to authorised functions |
| Loan repositories | Former lending staff retaining document access | High when confidential borrower records remain accessible | Remove outdated group membership |
| Reporting platforms | Bulk export of identifiable customer information | High when broad exports lack business justification | Restrict export and data scope |
| Collaboration folders | Sensitive documents shared across departments | Depends on sensitivity and audience | Review inherited permissions |
| Vendor support | Confidential data accessible after engagement ends | High when access is no longer authorised | Revoke and verify access removal |
| Service accounts | Broad access to production financial databases | Depends on privilege, purpose, and safeguards | Validate ownership and restrict permissions |
Use the matrix as an illustrative starting point and assess each finding against the institution’s systems, data sensitivity, and risk appetite.
How a Credit Union Can Correct Excessive Reporting Access
A hypothetical credit union uses a shared analytics workspace for lending reports containing borrower names, loan balances, account identifiers, and selected financial information. During a system migration, the credit union grants a broader employee group temporary access for testing. The permission remains active after migration, allowing other departments to open identifiable borrower records.
- Investigate effective access. Check direct permissions, inherited group memberships, and application roles. Reconcile the accounts with current employee and contractor records.
- Confirm the business need. Ask the reporting owner which departments need borrower-level information, branch-level summaries, or no continued access.
- Apply targeted restrictions. Give teams that need summaries access to appropriately restricted reports. Remove access to the sensitive workspace where there is no valid purpose and evaluate whether to restrict exports.
- Verify the outcome. Check direct and inherited access after the changes. Retain the original finding, business decision, implemented change, and verification evidence.
Why Sensitive Data Access Reviews Need More Than Account Lists
Two employees may legitimately use the same reporting application. One needs aggregated branch figures, while the other needs identifiable customer information for an authorised investigation. A sensitive data access review should capture:
- The identity and the resource or dataset it can reach.
- The permitted actions and whether access is direct or inherited.
- The business owner’s decision and justification.
- Evidence that any required restrictions took effect.
If a legacy banking or reporting system exposes only application-level permissions, record that visibility limit in the review.
How Data Classification, Identity Governance, and DLP Work Together
These controls answer different questions about where sensitive information sits, who can reach it, and what happens when it moves.
| Control | Primary function | Banking example |
| Data discovery and classification | Identify and categorise sensitive information | Locate repositories containing borrower identity documents |
| Identity governance | Review and govern who holds access rights | Certify permissions assigned to lending employees |
| Data access governance | Evaluate permissions in relation to accessible data | Identify broad access to sensitive shared folders |
| Data loss prevention (DLP) | Detect or restrict inappropriate data movement | Block an unauthorised transfer of financial records |
| Activity monitoring | Record or detect relevant access and usage behaviour | Investigate unusual data exports |
| Encryption | Protect information according to configured safeguards | Protect sensitive records in storage or transmission |
How to Evaluate Sensitive Data Access Management Solutions
Start with a real access question. Can the institution identify who can download confidential borrower information, confirm whether the access is justified, and verify that unnecessary permissions were removed?
| Evaluation area | What to verify |
| Data visibility | Whether the solution discovers sensitive data directly or uses classification from another system |
| Identity-to-resource mapping | Whether it connects employees, contractors, and service accounts to resources, including inherited access where supported |
| Permission detail | Whether reviewers can distinguish application access from access to specific datasets, resources, or functions |
| Review accountability | Whether decisions can be assigned to a manager, application owner, or data owner who understands the business need |
| Remediation and verification | Whether changes use a connector, ticket, or manual process and how the institution confirms the result |
| Evidence and reporting | Whether the institution can trace decisions, completed changes, and outstanding exposure |
A Practical Proof of Concept for One Sensitive Repository
Choose one high-risk reporting workspace, shared lending folder, or document repository. Include identities with different access needs.
| Test identity | Initial condition | Expected governance outcome |
| Current lending employee | Requires approved borrower information | Retain appropriate access |
| Transferred employee | Holds outdated lending permissions | Remove unnecessary access |
| Reporting analyst | Needs aggregate data, not identifiable records | Restrict information scope where supported |
| External contractor | Engagement has ended | Revoke expired access |
| Service account | Supports an active integration | Confirm ownership and required permissions |
Check whether the solution collects reliable access information, identifies owners, and follows corrective actions through verification. If the process relies on a separate classification tool, test how its data enters the review. Track resources with confirmed owners, reconciled accounts, verified revocations, and unresolved restrictions.
What Do Financial Information Security Requirements Mean for Access Governance?
The Gramm-Leach-Bliley Act establishes a framework for safeguarding certain customer information. Specific implementing requirements depend on the institution and its regulator. The FTC Safeguards Rule applies to covered institutions under FTC jurisdiction. Banks and federally insured credit unions generally operate under their respective banking agency or NCUA information security frameworks.
Access governance supports these programmes by linking permissions to business responsibilities, assigning owners, and preserving evidence of reviews and corrective actions. Institutions also need appropriate technical protection, operational controls, and oversight under their applicable requirements.
Where Identity Governance Supports Sensitive Data Protection
A lending employee may have access through a loan origination platform, directory group, reporting application, and shared repository. Reviewing those permissions together can reveal access that separate application reviews miss.
SecurEnds supports identity and entitlement visibility, certification workflows, and remediation reporting across connected applications. Confirm the resource-level detail available for each integration. User Access Reviews
Credit unions can also coordinate access governance across employees, contractors, and connected banking systems. Identity Governance for Credit Unions
Best Practices for Sensitive Data Access Management
- Start with a high-risk repository. Identify the information it contains, who owns it, and who can reach it.
- Review what permissions allow. Check whether users can export or share confidential data, including through inherited access.
- Reassess access after transfers and contract end dates. Include shared folders and reporting platforms alongside banking applications.
- Preserve access people still need. Use restricted or aggregate reports where those meet the business requirement.
- Verify changes at the resource. Confirm that affected users can no longer reach the restricted information through direct or inherited permissions.
Frequently Asked Questions
What is the difference between sensitive data access management and data access governance?
Sensitive data access management focuses on controlling who can reach confidential or regulated information and what they can do with it. Data access governance also covers the policies, ownership, review processes, and oversight behind those decisions.
Can a bank employee have appropriate application access but excessive data permissions?
Yes. An employee may need a reporting application while retaining the ability to view or export records outside their responsibilities. Review data scope, inherited roles, and export functions when certifying their access.
How can credit unions identify sensitive member information stored outside core banking systems?
Inventory shared folders, document repositories, reporting platforms, cloud storage, and connected applications. Data discovery and classification tools can help locate confidential records. Ask application and data owners to validate the findings and review who can access those resources.
Is read-only access to financial data always lower risk than editing access?
No. Read-only access may still let someone view, copy, or export large amounts of confidential information. Assess the sensitivity and scope of the data, available download functions, and business purpose.
Can identity governance software replace sensitive data discovery and DLP tools?
The functions differ. Identity governance helps establish who holds access, data discovery locates sensitive information, and DLP addresses inappropriate data movement. Some products integrate these capabilities, so verify the specific functions and integration depth available.
How should banks handle sensitive data access for contractors and service accounts?
Limit contractor access to authorised duties and an approved duration. Assign service accounts an accountable technical owner and scope permissions to operational needs. Verify access removal when the underlying requirement ends.
What should financial institutions measure to evaluate sensitive data access controls?
Track repositories with confirmed owners, excessive access findings, outdated permissions, open exceptions, and verified revocations. Check whether broad access decreased while authorised employees could still perform their work.